
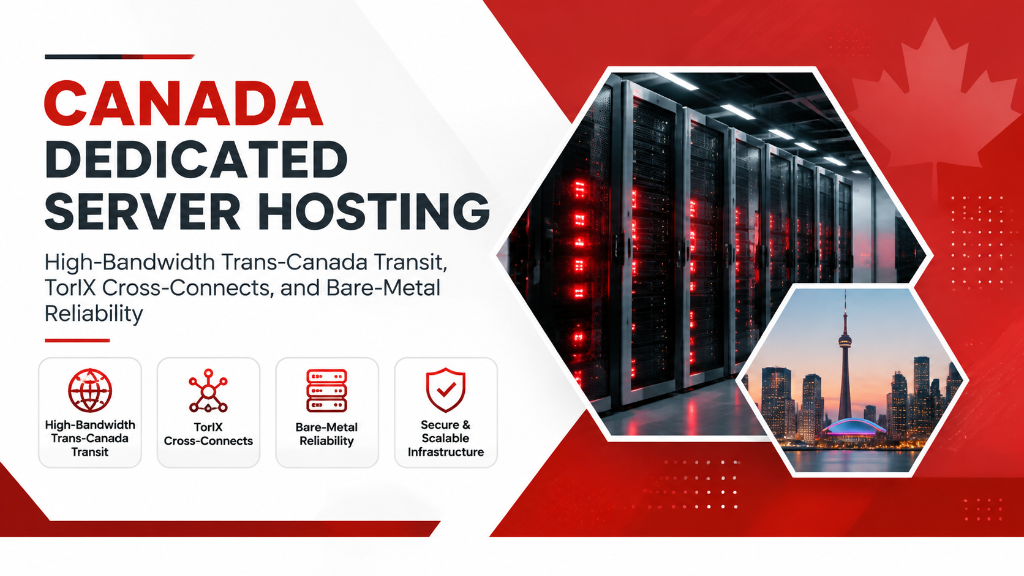
Deploying an enterprise Canada Dedicated Server in certified Toronto & Montreal data centers delivers direct local peering via TorIX & QIX, slashing latency for domestic visitors down to sub-15ms. Powered by dedicated AMD EPYC or Intel Xeon processors, unshared ECC RAM, and PCIe Gen4 NVMe RAID arrays, it provides guaranteed computing resources, regional data compliance, and 99.9% uptime for mission-critical digital workloads.
Explore our flexible VPS hosting plans for flexible virtualization.
- Low-Latency Interconnects: Direct routing through TorIX & QIX ensures deterministic response times across Canada and neighboring markets.
- Enterprise Hardware Isolation: Dedicated CPU execution threads and PCIe Gen4 NVMe arrays eliminate noisy-neighbor bottlenecks.
- Regional Compliance & Security: Localized data residency with in-line DDoS mitigation and 24/7 proactive technical operations.
Deploying dedicated bare-metal infrastructure in Canada provides enterprise software vendors, financial institutions, and high-concurrency database operators direct, unthrottled access to North American telecommunications backbones with absolute hardware autonomy. By establishing compute nodes in Toronto and Montreal, organizations secure deterministic memory latency, unshared storage controllers, and full root-level control over their network stacks. Bare-metal hosting in Canadian datacenters eliminates public cloud hypervisor contention, provides deterministic NVMe storage queues, and ensures strict adherence to PIPEDA and provincial privacy regulations. For mission-critical single-tenant workloads, deploy our high-availability cloud server infrastructure with unshared physical compute. For organizations scaling high-throughput compute workloads, our Canada dedicated server hosting infrastructure provides dedicated unmetered performance and enterprise hardware isolation.
Workloads hosted on dedicated bare-metal platforms avoid the CPU throttling and context-switching overhead imposed by shared hypervisors. Engineering teams retain direct control over physical CPU scheduling, memory NUMA allocations, and hardware network interface queues. Organizations transitioning to an Onlive Infotech dedicated server secure dedicated DDR5 ECC registered memory channels, direct PCIe Gen5 NVMe storage arrays, unmetered multi-gigabit uplinks, and complete root administrative privileges. When selecting a server administration interface, review our comprehensive Plesk vs cPanel control panel guide.
Canadian Telecommunications Topography and TorIX / QIX Peering Infrastructure
The network topography of Canadian enterprise hosting centers on Toronto (anchored by the 151 Front Street carrier hotel and Equinix TR1/TR2 campuses) and Montreal (including Equinix MT1 and Cologix MTL1-MTL11 campuses in downtown Montreal). Toronto functions as the financial telecommunications apex of Canada, while Montreal serves as a major artificial intelligence research and cloud colocation nexus powered by Hydro-Quebec clean energy.
Interconnection efficiency across Canada relies on direct cross-connections through domestic internet exchange points. The Toronto Internet Exchange (TorIX) and the Montreal Internet Exchange (QIX) serve as primary peering fabrics, handling high-capacity domestic traffic exchange. Connecting directly to these exchange fabrics provides single-hop routing to leading Canadian telecommunications operators and broadband service providers: Bell Canada (AS577), Rogers Communications (AS812), Telus (AS852), and Cogeco (AS11296). Domestic round-trip latency within Toronto metropolitan datacenters measures below 0.7 milliseconds. Transit between Toronto and Montreal measures under 7 milliseconds, transit to New York City registers under 9 milliseconds, and routing to Chicago stays under 13 milliseconds.
High-volume transit reliability is reinforced through autonomous BGP multi-homing. By combining direct peering across TorIX and QIX with redundant upstream links to international tier-1 transit operators (including Arelion, Lumen, and Tata Communications), bare-metal servers automatically bypass terrestrial fiber cuts. BGP routing engines recalculate optimal Autonomous System paths within milliseconds, preserving active TCP sessions and preventing packet loss during major carrier link maintenance.
Bare-Metal Compute Platforms: Microarchitectures and Memory Channels
Selecting the proper CPU microarchitecture is critical for sustaining execution throughput under continuous server workloads. Onlive Infotech bare-metal deployments in Canada utilize modern enterprise processor lines: AMD EPYC 9004 series (Zen 4 microarchitecture, Genoa and Bergamo) and 4th/5th Generation Intel Xeon Scalable processors (Sapphire Rapids and Emerald Rapids). These processors offer physical core allocations of up to 128 cores per socket, high-performance AVX-512 and Intel AMX vector execution engines, and extensive PCIe Gen5 lane connectivity.
Memory bandwidth is the decisive factor in high-throughput workloads including in-memory data caches, distributed search clusters, and transactional relational databases. Dual-socket AMD EPYC platforms feature 12 channels of DDR5 ECC registered memory per CPU socket, establishing 24 independent physical memory channels per motherboard. Running at speeds up to 4800 MT/s, this layout achieves theoretical memory bandwidth exceeding 460 GB/s per socket. This wide memory pipeline prevents core starvation when dozens of CPU cores process concurrent SQL queries or analytical data pipelines.
Infrastructure administrators can inspect hardware cache structures, NUMA domain configurations, and hardware security attributes directly via standard Linux command-line utilities:
Unlike virtualized public cloud instances where hypervisor vCPU scheduling introduces noisy-neighbor latency spikes, bare-metal servers offer absolute compute predictability. Operating systems can bind worker threads to specific physical CPU cores using processor affinity (`taskset` or `numactl`), eliminating Translation Lookaside Buffer (TLB) invalidation and L3 cache thrashing across heavy transactional workloads.
Storage Subsystem Architecture: Direct-Attached PCIe Gen5 NVMe
Modern enterprise data platforms require solid-state storage capabilities far beyond legacy SATA or SAS interfaces. Dedicated servers hosted in Canadian datacenters feature enterprise Non-Volatile Memory Express (NVMe) solid-state storage communicating directly with the CPU across PCIe Gen4 and Gen5 lanes. Bypassing legacy storage controller command queues drops I/O round-trip latency to under 12 microseconds for 4KB random reads.
Enterprise U.2 and E3.S NVMe drives deliver sustained sequential read throughput above 7,200 MB/s and random read metrics exceeding 1,200,000 IOPS per disk. In mission-critical environments, drives are configured in resilient software RAID arrays using the native Linux block layer (`mdadm`) or high-durability OpenZFS pools. This architecture ensures continuous data availability, online drive replacement, and automated background consistency verification without incurring the write-cache latency penalties associated with hardware RAID controller cards.
For organizations operating staging environments, microservices testing clusters, or secondary application layers that do not require dedicated physical drive arrays, an Onlive Infotech VPS hosting package offers an agile virtualized alternative with high-speed NVMe storage and root control.
Comparative Infrastructure Configurations
Aligning hardware specifications with specific workload profiles prevents both resource bottlenecks and unnecessary operating expenses. The matrix below outlines enterprise configurations tailored for deployment in Canadian datacenters: To achieve balanced multi-instance agility and cost efficiency, pair your deployment with Canada VPS server hosting solutions featuring high-speed NVMe storage arrays.
| Workload Classification | CPU Architecture | Memory (RAM) | Storage Layout | Network Port | Primary Use Case |
|---|---|---|---|---|---|
| Web Cluster & Microservices | Single AMD EPYC 8224P (24C/48T) | 64GB DDR5 ECC | 2x 960GB NVMe PCIe 4.0 (RAID1) | 1 Gbps Dedicated | High-traffic e-commerce, reverse proxy nodes, API gateways |
| Database & Transaction Core | Single AMD EPYC 9354 (32C/64T) | 128GB DDR5 ECC | 2x 1.92TB NVMe PCIe 5.0 (RAID1) | 2x 10 Gbps LACP Redundant | PostgreSQL, MySQL Enterprise, Redis clusters, financial ledger |
| Enterprise Virtualization | Dual Intel Xeon Gold 6430 (64C/128T) | 256GB DDR5 ECC | 4x 3.84TB NVMe PCIe 4.0 (RAID10) | 2x 10 Gbps LACP Redundant | Proxmox VE, VMware ESXi, OpenStack private cloud nodes |
| Big Data & AI Fine-Tuning | Dual AMD EPYC 9554 (128C/256T) | 512GB DDR5 ECC | 8x 7.68TB NVMe U.2 Hot-Swap | 2x 25 Gbps Redundant | ClickHouse analytics, Elasticsearch cluster, AI inferencing |
| Edge Compute & Streaming | Single Intel Xeon E-2388G (8C/16T) | 32GB DDR4 ECC | 2x 512GB NVMe PCIe 3.0 (RAID1) | 1 Gbps Unmetered Port | Live RTMP transcoding, audio streaming, DNS authoritative |
For early-stage startups, personal portfolios, or simple static business websites where dedicated physical hardware is not yet required, a managed Onlive Infotech web hosting plan provides a turnkey solution with cPanel management and automated backups.
Linux Kernel Network Optimization for Trans-Canadian Peering
Bare-metal servers equipped with 10Gbps or 25Gbps network interfaces require explicit kernel-level tuning to reach maximum line-rate throughput. Default Linux distribution configurations are configured with conservative socket buffers designed for general desktop use or 1Gbps interfaces, leading to artificial TCP window throttling during volumetric data transfers.
Enabling Google BBR (Bottleneck Bandwidth and RTT) congestion control improves throughput over high-capacity cross-border connections compared to traditional loss-based algorithms like Cubic. The configuration below adjusts the Linux networking stack for optimal multi-gigabit performance:
Network interface controllers also require ring buffer adjustments to handle sudden inbound traffic spikes without dropping packets at the physical framing layer. Executing `ethtool -G eth0 rx 4096 tx 4096` expands the network controller hardware buffer to its maximum supported capacity, preventing buffer overruns during peak traffic periods.
Out-of-Band Hardware Telemetry and IPMI Management
Operating critical server infrastructure in Canadian colocation facilities requires total administrative autonomy through isolated Out-of-Band (OOB) management channels. Enterprise servers feature dedicated Intelligent Platform Management Interface (IPMI 2.0), Dell iDRAC, or Supermicro IPMI/BMC controller hardware. These microcontrollers operate independently of the host operating system, powered via standby motherboard circuitry and connected to physically isolated management VLANs.
Through the IPMI interface, systems administrators can perform low-level hardware diagnostics, mount virtual ISO installation images, adjust UEFI settings, power-cycle frozen operating systems, and capture kernel crash logs without requiring onsite datacenter technician intervention.
This independent hardware management layer provides complete operational control. Engineering teams can rebuild operating systems remotely, diagnose degraded memory modules, and monitor power consumption without filing datacenter support tickets.
Data Sovereignty, PIPEDA, and Quebec Law 25 Compliance
Deploying infrastructure in Canada provides strong statutory data sovereignty protections under federal and provincial privacy frameworks:
- PIPEDA Compliance: The Personal Information Protection and Electronic Documents Act establishes strict principles for commercial data collection and processing. Storing customer information in Canadian datacenters insulates data from foreign extra-judicial access regimes such as the US CLOUD Act.
- Quebec Law 25 (Act Respecting the Protection of Personal Information): Imposes strict GDPR-aligned requirements including mandatory privacy impact assessments (PIAs) before transferring personal information outside Quebec, strict incident logging, and substantial penalties for data breaches.
- SOC 2 Type II and ISO 27001 Datacenters: Montreal and Toronto facilities maintain third-party security audits validating environmental controls, multi-factor biometric site access, and continuous power resilience.
- Renewable Clean Energy Standards: Montreal facilities draw power directly from Hydro-Quebec’s 99.8% renewable hydroelectric grid, supporting organizational ESG (Environmental, Social, and Governance) targets.
DDoS Defense and Perimeter Network Protection
Bare-metal servers deployed in Canadian network hubs face continuous exposure to volumetric and protocol-based distributed denial-of-service (DDoS) attempts. Without upstream scrubbing, large attacks can saturate uplink bandwidth and disrupt business operations.
Onlive Infotech provides multi-stage automated DDoS scrubbing arrays integrated directly into Canadian network edge points of presence. Inbound traffic undergoes continuous packet inspection, identifying and neutralizing malicious traffic within milliseconds of detection:
Volumetric attacks exceeding 500 Gbps are scrubbed upstream at edge routers before reaching local rack switches. This multi-layered defense ensures that host network ports remain available for legitimate users while local software firewalls (configured via `nftables`) handle host-specific rate-limiting and application-level access control.
Frequently Asked Questions
Q:
Why choose Canada for dedicated server hosting over the United States?
Q:
What latency can be expected between Montreal, Toronto, and New York?
Q:
Can I configure software RAID arrays and full disk encryption on NVMe storage?
Q:
What administrative privileges are granted with the dedicated server?
Q:
Which operating systems can be deployed on the bare-metal hardware?
Infrastructure Decision Framework: Choosing Your Deployment
Balancing low latency transit, dedicated hardware isolation, and predictable operating costs ensures long-term performance stability for enterprise applications.
Deploy high-performance enterprise dedicated server solutions equipped with enterprise NVMe storage arrays, redundant network uplinks, and 24/7 expert engineering support from Onlive Infotech.
For streamlined domain management and server configuration across multi-tenant environments, refer to our comprehensive Plesk vs cPanel hosting control panel guide.
•
✓
